Local Grocery Store Could Be a Target

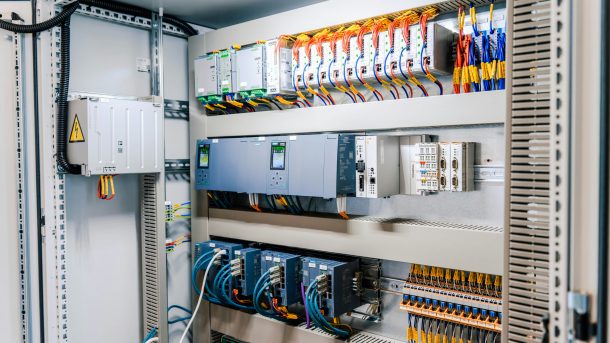
Photo by Franki Chamaki on Unsplash

Your local supermarket is an OT environment.

And your food just got hacked.

Attackers forced food freezers into defrost mode.

At nearly 100 grocery stores at once.

-> Ruined food.
-> Heavy food losses.
-> Setting small fires.
-> Causing chaos and confusion.

Attacks against OT and ICS environments are increasing.

Not only in number, but in impact.

Before, a single store might have been hit.

Now it’s almost 100 at once.

Think of how this might impact other areas.

-> 100 power plants
-> 100 subway trains
-> 100 desalination plants
-> 100 electric substations
-> 100 manufacturing sites
-> 100 food processing plants
-> 100 water treatment facilities

This list can go on forever.

It impacts so much more.

Ultimately, it impacts our families, friends, and communities.

If you’re responsible for an environment like this, start here:

-> List out each controller you have and its firmware version
-> Determine if they can be reached from the Internet
-> Look to see if there are any known vulnerabilities on the controllers
-> Update the firmware as necessary
-> Change default credentials
-> Remember updates aren’t everything – keep access limited
-> Set up out-of-band alerting systems to tell you if your temperature is too high

Protecting OT from cyber attacks doesn’t have to be complicated.

But we still have to put in the work and close our security gaps.

Before the attackers find them.

And take advantage of them.

Even inside our grocery stores.

How AI SOC Analysts Move SecOps Into The Future

Photo by Lazar Stankovic on Unsplash

Triaging and investigating alerts are crucial parts of security operations. As Security Operations Center (SOC) teams face increasing alert volumes and complexities, modernizing SOC automation with AI has become essential. This blog explores how an AI SOC Analyst can transform alert management by tackling key challenges SOC teams face and enabling faster investigations and responses.

Security operations teams face constant pressure to manage an overwhelming influx of security alerts generated by a growing number of tools. Each alert can have serious consequences if ignored, yet most are false positives. This deluge traps teams in a cycle of tedious, repetitive tasks that drain time and resources. As a result, stretched-thin teams struggle to balance reactive alert response—often described as a “whack-a-mole” approach—with proactive threat hunting and other strategic security initiatives.

Core Challenges

High alert volumes: Security operations teams receive hundreds to thousands of alerts a day, making it nearly impossible for analysts to keep up. For many SOCs, this overload causes delayed response times and forces teams to make tough decisions about which alerts to prioritize.

Manual, repetitive tasks: Repetitive, manual tasks burden traditional SOC workflows, requiring analysts to sift through logs, switch between tools, and manually correlate data. These inefficiencies delay alert investigations and incident response and exacerbate analyst burnout and turnover.

Hiring and training challenges: A global shortage of cybersecurity talent makes it difficult for SOCs to recruit and retain skilled professionals. High analyst turnover, driven by burnout and demanding workloads, further compounds the issue.

Limited proactive threat hunting: Because many SOCs are reactive, proactive efforts like threat hunting often take a backseat. With so much time consumed by alert management and incident response, few teams have the bandwidth to actively hunt for undetected threats.

Missed detections: Time and talent shortages lead many SOCs to ignore “low- and medium-severity” alerts altogether or turn off detections, exposing the organization to additional risk.

Unrealized promises of SOAR: Security Orchestration, Automation, and Response (SOAR) solutions have aimed to automate tasks but often fail because they require extensive playbook development and maintenance. Many organizations struggle to fully implement or maintain these complex tools, leading to patchwork automation and continued manual work.

MDR/MSSP challenges: MDR/MSSP vendors lack the enterprise context needed to investigate custom detections accurately. Additionally, these vendors often operate as expensive black boxes, offering investigations and responses with little transparency, making it hard to verify their accuracy or quality.

The rise of AI-powered attacks

Traditional, manual SOC processes already struggling to keep pace with existing threats are far outpaced by automated, AI-powered attacks. Adversaries use AI to launch sophisticated, targeted attacks, putting additional pressure on SOC teams. To defend effectively, organizations need AI solutions that can rapidly sort signals from noise and respond in real time. AI-generated phishing emails are now so realistic that users are more likely to engage, leaving analysts to untangle the aftermath—deciphering user actions and gauging exposure risk, often with incomplete context.

Advances in LLMs and agentic architectures

The emergence of large language models (LLMs), generative AI, and agentic frameworks has introduced a new level of reasoning and autonomy for security operations center (SOC) automation tools. Unlike traditional, static, rule-based playbooks, these advanced approaches can dynamically plan, reason, and learn from analyst feedback. This ongoing refinement improves investigations over time, leading to an AI-driven SOC.

The Case for AI SOC Analysts

Streamlined investigations

AI SOC Analysts investigate every alert within minutes, analyzing data across endpoints, cloud services, identity systems, and other data sources to filter false positives and prioritize true threats.

Lower risk

Faster investigation and remediation minimize the potential damage of a breach, reducing costs and reputational risk. Proactive hunting further mitigates the likelihood of hidden compromises.

Seamless integration

An AI SOC Analyst integrates seamlessly with popular SIEM, EDR, Identity, Email, and Cloud platforms, plus case management and collaboration tools, out of the box. This allows for rapid deployment and minimal disruption to existing processes.

Improved SOC metrics

By leveraging AI SOC Analysts, security operations teams can overcome key challenges and measurably improve critical SOC metrics.

  • Lower dwell time: Automated investigations allow the SOC to spot threats before they spread.
  • Reduced MTTR/MTTI: AI’s rapid triage and analysis slashes the time needed to investigate and respond to alerts.
  • Enhanced alert coverage: Every alert is investigated, ensuring no threat goes ignored. By automating alert triage and investigation, organizations can drastically reduce dwell time, mean time to investigate (MTTI), and mean time to respond (MTTR).

Empowered teams

An AI SOC Analyst is a powerful force-multiplier for the SOC. By removing the burden of manual, repetitive tasks, analysts can focus on higher-value work like threat hunting and strategic security initiatives. This not only boosts morale but also helps attract

Scalability

AI SOC Analysts operate 24/7 and scale automatically with alert volume. Whether an organization sees hundreds or thousands of alerts daily, AI can handle the load without additional staff.

Future of SecOps: Human and AI collaboration

The future of security operations lies in seamless collaboration between human expertise and AI efficiency. This synergy doesn’t replace analysts but enhances their capabilities, enabling teams to operate more strategically. As threats grow in complexity and volume, this partnership ensures SOCs can stay agile, proactive, and effective.
IT vs. OT Cybersecurity: What’s the Difference?

Photo by Raymond Sime on Unsplash

IT and OT cybersecurity are closely related, but they protect different environments and require different security approaches.

  1. IT Cybersecurity (Information Technology)

IT security protects data, applications, and business systems.

Examples:

  • Laptops, servers, and databases
  • Cloud platforms and business applications
  • Corporate networks and email systems
  • Identity and access management

Key priorities: Confidentiality, Integrity, and Availability (CIA).

Common threats include ransomware, phishing, data breaches, and credential theft.

  1. OT Cybersecurity (Operational Technology)

OT security protects systems that monitor and control physical processes in industrial environments.

Examples:

  • PLCs (Programmable Logic Controllers)
  • SCADA systems
  • DCS (Distributed Control Systems)
  • HMIs, sensors, and industrial controllers
  • Manufacturing and production equipment

Key priorities: Safety, Availability, Reliability, and Process Integrity.

Common threats include unauthorized changes to control logic, disruption of industrial processes, and compromise of remote access.

  1. Key Differences

IT incidents can cause data loss, financial damage, and business disruption.

OT incidents can also stop production, damage equipment, affect the environment, or create safety risks.

Carefully evaluate patching, rebooting, and active vulnerability scanning in OT environments because they can disrupt critical industrial processes.

  1. Why IT/OT Convergence Matters

As industrial environments become more connected, compromised IT systems can create pathways into OT networks.

Effective protection requires network segmentation, restricted remote access, continuous monitoring, secure configurations, and coordinated incident response.

Standards and guidance such as IEC 62443 and NIST SP 800-82 help organizations develop appropriate industrial cybersecurity practices.

The Bottom Line

IT protects digital business operations.

OT protects physical industrial operations.

Both are essential, and securing them requires collaboration between IT, cybersecurity, engineering, and operations teams.

SOC Analysts: How AI Transforms the Modern SOC

Photo by Jakub Żerdzicki on Unsplash

As cyber threats grow more sophisticated, organizations must strengthen their defenses to protect sensitive data and maintain operational integrity. At the center of this defense is the Security Operations Center (SOC), staffed by dedicated SOC analysts. But what exactly is a SOC analyst, and how is their role evolving with new technologies like artificial intelligence (AI)?

This article clarifies a SOC analyst’s responsibilities and explores how AI is transforming the modern SOC to address today’s dynamic cybersecurity challenges.

What Is a SOC Analyst?

A SOC analyst is a cybersecurity professional who monitors, detects, and responds to security incidents within an organization’s IT infrastructure. They serve as the frontline defenders against cyber threats, working within the SOC to safeguard the organization’s assets

SOC Analyst Meaning

The term “SOC analyst” encompasses various levels of expertise and responsibilities, often structured in tiers:

  • Tier 1 SOC Analyst: Focuses on initial incident triage, monitoring alerts, and identifying potential security incidents.
  • Tier 2 SOC Analyst: Performs deeper analysis of validated incidents, using advanced SOC tools and methodologies to assess scope and impact.
  • Tier 3 SOC Analyst: Specializes in threat hunting, coordinating incident response, and developing long-term security strategies.

Integrating artificial intelligence into the SOC is reshaping SOC analysts’ roles and helping address many of the challenges they face.

AI SOC Solutions

AI SOC solutions use machine learning and AI algorithms to analyze vast amounts of data faster and more accurately than humans can. They identify patterns and anomalies that may indicate a security threat.

SOC Automation

SOC automation uses AI to automate repetitive, time-consuming tasks, such as log analysis and initial incident triage. This automation lets SOC analysts focus on more complex, strategic work.

Enhanced Incident Triage and Response

AI tools can perform initial incident triage, assessing alerts for validity and severity. They can also suggest remediation steps, accelerating response.

Enrichment in Threat Intelligence

AI enhances threat intelligence enrichment by automatically gathering and correlating data from various sources. This gives SOC analysts comprehensive context on potential threats.

Benefits of AI Integration in the SOC

Reducing Alert Fatigue

By automating security alert analysis and filtering out false positives, AI reduces the number of alerts SOC analysts must investigate manually, alleviating alert fatigue.

Enhancing Efficiency and Accuracy

AI processes data at speeds unmatched by humans, increasing the efficiency of threat detection and response. It also improves accuracy by minimizing human errors.

Enabling Proactive Threat Hunting

AI can identify patterns and indicators of compromise that may not be apparent to human analysts, enabling more effective proactive threat hunting.

Supporting Skill Development

With AI handling routine tasks, SOC analysts have more time to focus on skill development and strategic initiatives, addressing the skill shortage by maximizing existing talent.

The Future of SOC Analysts in the Age of AI

Evolving Roles

As AI takes over routine tasks, SOC analysts will evolve into more strategic roles, focusing on:

  • Advanced Threat Analysis: Investigating complex threats that require human intuition and expertise.
  • Security Strategy Development: Designing and implementing security architectures and policies.
  • Collaboration and Communication: Working across departments to enhance organizational security awareness.

Embracing Continuous Learning

SOC analysts will need to continually update their skills, learn to work alongside AI tools, and understand emerging technologies and threats.

AI as a Collaborative Tool

Rather than replacing SOC analysts, AI serves as a powerful tool that enhances their capabilities. The synergy between human expertise and AI efficiency leads to a more robust cybersecurity posture.

Conclusion

The SOC analyst role is more critical than ever in defending organizations against sophisticated cyber threats. Understanding the SOC analyst role, its responsibilities, and its importance provides insight into the backbone of modern cybersecurity operations.

Integrating AI SOC solutions and SOC automation is transforming the modern SOC. By reducing alert fatigue, improving efficiency, and enabling proactive threat hunting, AI lets SOC analysts focus on strategic initiatives that strengthen an organization’s security posture.

As the cybersecurity landscape evolves, embracing AI technologies is not just advantageous—it’s essential. Organizations that integrate AI into their SOC operations can better combat current and future cyber threats.

Autonomous SOC (ASOC) 101

Photo by Jade Chambers on Unsplash

Frontier AI is changing cybersecurity at a pace the industry has never seen before. Threat actors are now leveraging Frontier AI to accelerate attacks, evade traditional defenses, and compress the time organizations have to react from hours to minutes, and in many cases, seconds.

Modern cyberattacks move at machine speed. Attackers now use AI-powered tools to launch phishing campaigns, exploit vulnerabilities, and move laterally across networks faster than human analysts can respond.

Unfortunately, most Security Operations Centers still operate using a reactive model:

  • Analysts manually triage alerts
  • Investigations take 30-40 minutes or longer
  • Alert backlogs grow faster than teams can respond
  • Skilled security talent is difficult to hire and retain

The Result:

  • Increased breach risk
  • Operational disruption
  • Escalating security thoughts

Organizations need a security mode designed for the speed of modern threats.

ASOC was not built in response to hype. It was built from years of real-world cybersecurity experience, operational expertise, and a deep understanding of how modern threats evolve. Security professionals recognized early that defending against machine-speed attacks would require machine-speed operations.

Introducing the Autonomous SOC

The next evolution of security operations.

Instead of relying solely on human analysts, ASOC introduces an agentic AI layer that continuously analyzes security telemetry across your entire environment.

This AI layer:

  • Correlates signals across security tools
  • Investigates alerts automatically
  • Calculates risk and confidence scores
  • Executes containment actions when safe
  • Escalates complex incidents to human analysts

The result is faster response, reduced workload, and stronger resilience. ASOC transforms cybersecurity from reactive detection into pre-emptive defense.

The fundamentals of cybersecurity still matter. Visibility, detection engineering, rapid response, and continuous monitoring remain critical. What has changed is the speed required to operationalize them.

ASOC enables organizations to:
• Detect threats faster
• Investigate incidents at scale
• Contain attacks in seconds
• Reduce operational fatigue
• Improve resilience against Frontier AI-driven threats

AI is no longer optional in cybersecurity defense models. Adversaries are already using it. Organizations that embrace responsible AI-driven defense will be best positioned to protect their operations, customers, and critical infrastructure.

Attack Surface Reduction: Building More Secure Applications

Photo by Madeline Liu on Unsplash

Like hairline fractures spreading through glass, software vulnerabilities creep through code. At the bootcamp, developers spot these security holes daily – from rookie mistakes to deeply buried flaws.

We’ve watched teams rush out features, unaware they’re building perfect entry points for attackers. Each function needs proper hardening, but most think they’ll patch it “later.” That later rarely comes. While we guard a thousand doors, attackers just need one unlocked window.

Key Takeaways

  • Find those sneaky entry points – from sloppy code to settings nobody checked
  • Get the basics right: kill unnecessary services, lock down permissions, patch regularly
  • Watch everything, train everyone, automate what makes sense

What Makes Up an Attack Surface?

Every app has weak points; we see students stumble into them weekly. The usual suspects? Wide-open network ports nobody bothered to check, APIs leaking data like a broken faucet, and those bits of legacy code everyone’s scared to update. Our teaching team could probably write a book just about the creative ways developers accidentally leave systems exposed.

Mapping It All Out

Cutting corners on the boring stuff always comes back to bite you. Through years of training developers, we’ve nailed down what actually works:

  • Write down everything about the code and configs
  • Track where data flows (yeah, even the ugly parts)
  • Keep tabs on outside dependencies

Teams that understand how to minimize attack surface learn that these simple habits block attackers before they ever get in.

New features change everything – what worked yesterday might leave gaps today. The bootcamp’s seen countless teams learn this lesson. Some patterns just keep repeating, no matter how many times we warn them.

Techniques to Minimize Application Attack Surface: Real Fixes That Work

Security audits teach hard lessons – spotting problems isn’t enough. Every week our bootcamp students learn this the hard way. Exploring proven Attack Surface Reduction Techniques helps teams fix issues

Locking Down the Basics

Nothing fancy here, just common sense that’s uncomfortably rare. Dev servers shouldn’t face the internet, period. Those admin dashboards from three sprints ago? Gone. Our students get tired of hearing it, but the obvious stuff bites hardest.

Clearing Out the Junk

Dead code kills. Found that out when a student’s forgotten test API nearly leaked their entire customer database last month. Here’s what actually needs watching:

  • Dependency bloat nobody talks about
  • Test endpoints that outlived their purpose
  • Ancient systems running on hopes and prayers

Building Better Walls

Nobody gets excited about network segments, but they save jobs. Think compartments on a ship – breach one, not all. These basics keep working:

  • Lock down those permissions (yes, even for Bob in accounting)
  • Patch everything (servers don’t care about your weekend)
  • Watch the logs (they’re trying to tell you something)

Some things feel like overkill until they’re not. Good security fits the workflow – if it doesn’t, nobody uses it.

Conclusion 

Security isn’t a box to check; it’s alive and hungry. Years in the bootcamp taught us this: knowing your weak spots is half the battle. Start simple, map your assets, trim excess permissions, and patch like clockwork. It’s not glamorous, but we’ve watched “secure” apps crumble from tiny oversights. Put more eyes on the glass, automate what you can, and catch trouble early.

6 Ways to avoid a Punycode attack

Photo by Arsyad Basyarudin on Unsplash

Research shows a new phishing site is created every 20 seconds and they are usually only live for four hours before hackers take them down and move on to create another deceiving domain. A clever way to cover their tracks and evade detection.

  1. Be cautious if the site presses you to do something quickly. This is a classic strategy by hackers to rush their potential victims so that they are less likely to notice anything suspicious. Often they will offer a “limited time only” deal, and make it difficult to exit the page with ‘are you sure you want to exit’ pop-ups: these are all tactics to make you stay on their site longer and give them your details.
  2. If you are being offered a deal, go to the original company site and check if it’s available there as well, if not it’s most likely a scam doing its best to mimic the established brand and trick visitors into handing over their details.
  3. If some of the letters in the address bar look weird, or the website design looks different, rewrite it or visit the original company URL in a new tab to compare. The letters in the address bar looking strange is a key indicator that punycode is being used to trick you into thinking you are visiting a well-established brand site when in fact you are being taken to a malicious site.
  4. Use a password manager; this reduces the risk of pasting passwords into dodgy sites.
  5. Force your browser to display Punycode names, this option is available in Firefox.
  6. Click on the padlock to view and inspect the HTTPS certificate.

Wireless Vulnerabilities

Photo by Dede Erwanto on Unsplash

Wireless transmissions are inherently vulnerable to several attack vectors:

  • Data Emanation: Electronic signals radiating from devices can be intercepted and reconstructed into readable data, potentially exposing sensitive information.
  • Jamming/Interference: Devices such as cordless phones can disrupt wireless signals, compromising network availability through radio-frequency interference.
  • Packet Sniffing: Using only a wireless network adapter and packet-sniffing software, attackers can easily intercept Wi-Fi traffic. To safeguard sensitive data, organizations must implement strong encryption for all wireless communications.

War Driving and War Chalking

One of the most well-known wireless vulnerabilities is war driving, where attackers drive through areas with wireless-enabled devices to detect and map available wireless networks.

War chalking is a related practice where individuals use chalk to draw symbols on exterior building walls or sidewalks, marking the locations and details of discovered wireless networks. These symbols communicate different network characteristics to others in the war-driving community – for example, different markings might identify an open network (available to anyone), a closed network (with a visible SSID but requiring authentication), or a WEP-secured network.

SSID Broadcasting

A common security weakness in wireless networks is SSID broadcasting. When enabled, this feature makes your network easily discoverable by any nearby wireless device. To strengthen your security posture, you should always change the default SSID to something non-descriptive and disable SSID broadcasting on your wireless router.

WPS and Replay Attacks

There are two additional attack methods that pose significant risks to wireless networks:

  • WPS Attack: Wi-Fi Protected Setup (WPS) is designed to simplify connecting to a wireless network by using a PIN on the router. Once the PIN is entered, the SSID and WPA2 encryption key are configured automatically. However, a 2011 vulnerability allows attackers to brute-force the WPS PIN, compromising network security.
  • Replay Attack: A replay attack involves capturing legitimate network traffic and retransmitting it later to bypass authentication or crack encryption. Rather than attempting to decrypt captured packets, attackers simply replay previously recorded authentication sequences to gain access.

Rogue Access Points and Evil Twins

Rogue access points represent one of the most serious security threats to organizational networks, and are particularly important to understand for the Security+ exam. These unauthorized wireless access points are typically connected to the network without the IT department’s knowledge or approval – for example, when an employee installs a personal wireless router in their office to get better WiFi coverage.

Such rogue devices create dangerous security gaps because they often lack proper security configurations, allowing attackers to bypass the organization’s perimeter defenses. Network administrators must implement continuous monitoring to detect and remove any unauthorized access points.

For exam preparation, remember that regular wireless scanning with tools such as Acrylic WiFi, Cain & Abel, or Kismet is essential for identifying rogue access points in your environment.

Weak Encryption

The use of weak or outdated encryption protocols remains one of the most critical vulnerabilities in wireless security. WEP encryption is especially dangerous because its 24-bit Initialization Vector (IV) repeats frequently, enabling attackers to crack the encryption key in minutes using readily available tools.

While WPA and WPA2 offer stronger protection than WEP, they have also been compromised through various attacks. Currently, WPA3 provides the most robust security, but it should still be supplemented with additional protections.

For the Security+ exam, it’s crucial to remember that all wireless clients should be treated as potentially untrusted. Implementing a VPN solution provides an essential additional layer of security by encrypting all communications between wireless devices and the corporate network.

Three Types of Deserialization

Photo by ANOOF C on Unsplash

Serialization and deserialization are processes used in computer science and software development to convert complex data structures or objects into a format that can be easily stored, transmitted, or reconstructed later. These processes are particularly important when data needs to be passed between different parts of a program or across a network. Here’s an explanation of serialization and deserialization:

Serialization

Serialization is the process of converting a data structure or object in memory into a linear format that can be easily stored in a file or transmitted over a network. This linear format is typically a sequence of bytes or a text-based representation like JSON or XML. Serialization allows you to save an object’s state so it can be reconstructed later. The primary purposes of serialization include:

1. Data Persistence: Saving an object’s state to a file or a database so that it can be retrieved and used at a later time.

2. Data Transmission: Sending an object across a network to another application or system.

3. Cross-Language Communication: Facilitating communication between programs written in different programming languages.

Common use cases for serialization include saving user preferences in an application, storing game progress, and transmitting data between a client and server in web applications.

Deserialization

Deserialization is the reverse process of serialization. It involves taking the serialized data (e.g., a byte stream or JSON string) and reconstructing the original data structure or object in memory. In essence, deserialization is the process of turning data back into a usable form. The main purposes of deserialization are:

1. Data Retrieval: Loading data that was previously serialized, allowing it to be used within an application.

2. Data Processing: Processing data received over a network or from external storage and converting it into an internal data structure that an application can work with.

3. Cross-Language Communication: Converting data received from other systems or languages into a format that can be used by the local application.

What is Punycode?

Photo by Mika Baumeister on Unsplash

Punycode
noun
Unicode that converts words that cannot be written in ASCII, like the Greek word for thank you ‘ευχαριστώ’ into an ASCII encoding, like ‘xn--mxahn5algcq2e’ for use as domain names.
What does this actually mean?!

Writing with numbers

As with all things computers, it all boils down to numbers. Every letter, character, or emoji we type has a unique binary number associated with it so that our computers can process them. ASCII, a character encoding standard, uses 7 bits to code up to 127 characters, enough to code the Alphabet in upper and lower case, numbers 0-9 and some additional special characters. Where ASCII falls down is that it does not support languages such as Greek, Hebrew, and Arabic for example, this is where Unicode comes in; it uses 32 bits to code up to 2,147,483,647 characters! Unicode gives us enough options to support any language and even our ever-growing collection of emojis.

So where does Punycode come in?

Punycode is a way of converting words that cannot be written in ASCII, into a Unicode ASCII encoding. Why would you want to do this? The global Domain Name System (DNS), the naming system for any resource connected to the internet, is limited to ASCII characters. With punycode, you can include non-ASCII characters within a domain name by creating “bootstring” encoding of Unicode as part of a complicated encoding process.